Aegis Authenticator review — open-source 2FA for Android
Aegis is an open-source 2FA app for Android: encrypted local storage, biometric unlock, no account and no cloud. The natural replacement for Google Authenticator or Authy.
Aegis Authenticator review
Aegis is an open-source 2FA app for Android: encrypted local storage, biometric unlock, no account and no cloud. The natural replacement for Google Authenticator or Authy.
Who is this for? Android users who want a better 2FA app than Google Authenticator or Authy — open-source, encrypted backup, no cloud connection. See the 2FA guide for context on which method fits your situation.
Aegis is an open-source authenticator app for Android supporting TOTP and HOTP. Encrypted local storage, biometric unlock, no account required, no cloud connection. The default choice for anyone wanting to replace the 2FA codes of Google Authenticator or Authy.
Why 2FA at all?
Two-factor authentication adds a second security layer alongside your password. Even if an attacker knows your password, they also need access to your second factor. TOTP (Time-based One-Time Password) generates a new code on your device, usually six digits and by default every 30 seconds, without an internet connection.
What Aegis does better than alternatives
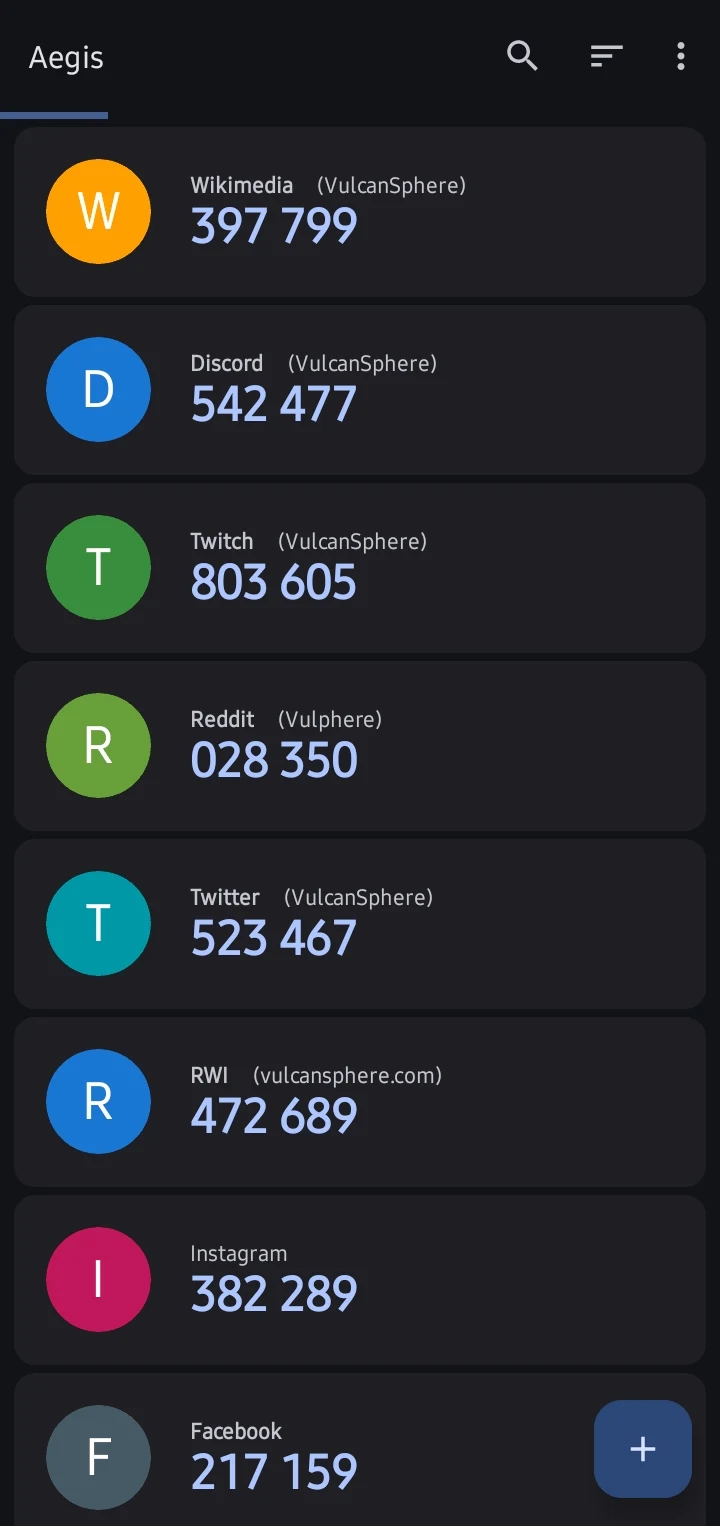
Aegis 3.2 in dark mode: one card per account, each with its current six-digit code. Screenshot: VulcanSphere, Wikimedia Commons (GPLv3).
Encrypted backup: Aegis can export your vault encrypted and can also back it up automatically, to a folder you choose, whenever something changes. By default, exports and backups use your vault password; under Settings → Security you can set a different one (Separate password for backup & export). If your phone breaks, import the backup on a new device and immediately regain access to your codes. Google Authenticator can now be used without an account, but then the only way to move your codes is its QR-code transfer from the old phone. Its backup route is syncing to your Google Account, which Google says it encrypts in transit and at rest.
No cloud connection: Aegis has no internet access at all, and its developers don’t plan to change that. You manage the backup. Advantage: no risk of account lockout at a third party. Disadvantage: you are responsible for getting a copy off your phone (see Backup strategy).
Biometric unlock: When you choose a password at setup, the vault is encrypted (AES-256-GCM, with the key derived from your password by scrypt). The None option leaves the vault unencrypted; Aegis itself advises against it. Biometric unlock uses a key in the Android Keystore that only works after you authenticate with your fingerprint or face, so the codes stay encrypted until you unlock, even if someone has your phone. On some phones with buggy implementations biometric unlock doesn’t work, according to the Aegis FAQ. Aegis asks for the password now and then anyway (the password reminder), because forgetting it means losing the vault.
Import from other authenticators: Aegis 3.4.3 reads export files from 2FAS, Proton Authenticator, FreeOTP 2, andOTP and a few other apps, and unencrypted exports from Bitwarden and Ente Auth. Google Authenticator works through its transfer QR code, which Aegis scans. Authy and Microsoft Authenticator can only be imported from the app’s internal data, which needs a rooted phone (Steam too, and not from Steam 3.0 or newer). The import screen in Aegis lists every supported app.
Open-source: Full source code available on GitHub. Independently auditable.
Who makes Aegis (as of November 2026)
Aegis is published under the name Beem Development by two developers, Alexander Bakker and Michael Schättgen. Both list the Netherlands on their GitHub profiles. Between them they wrote almost all of the code (1,064 and 496 contributions; no one else has more than 15). The project started in 2016.
Development is slow but steady: 22 code changes and two releases in the past twelve months (3.4.2 in February 2026, 3.4.3 on 6 September 2026). For a mature app with a narrow job that is not a warning sign in itself, but it does mean fixes depend on two people. Aegis is funded by donations (Buy Me a Coffee, Bitcoin and Nano, per its GitHub page); it lists no other funding.
Update to 3.4.3 or later. That release fixed a bug where a maliciously crafted icon pack could overwrite Aegis’s internal files, including the vault, if you imported it. F-Droid shipped 3.4.3 too (F-Droid builds Aegis itself; the developers say a new version can take up to a week to appear there).
Specifications
| Property | Value |
|---|---|
| Platform | Android (also on GrapheneOS) |
| Protocols | TOTP, HOTP |
| Backup | Encrypted or plaintext export; automatic encrypted backups to a folder you choose; optional Android cloud backup |
| Biometric | Yes (key in the Android Keystore) |
| Open-source | Yes (GPLv3) |
| Cloud sync | No (no internet access) |
| Price | Free |
| Availability | Play Store, F-Droid, GitHub APK |
Comparison with alternatives
| Aegis | Google Authenticator | Authy | Bitwarden (TOTP) | |
|---|---|---|---|---|
| Open-source | Yes | No | No | Yes |
| Encrypted backup | Yes | Sync to Google Account (optional) | Optional (cloud) | Yes |
| Cloud-independent | Yes | Optional (works without an account) | No | Depends |
| Biometric | Yes | Yes | Yes | Yes |
| Platform | Android | Android, iOS | Android, iOS | All |
| Free | Yes | Yes | Yes | Premium |
Authy has an optional encrypted backup to its cloud (Authy’s features page), and you add devices to an Authy account. That is convenient as a fallback, but less attractive for higher-risk profiles that want no cloud link.
Bitwarden TOTP (premium) is convenient if you want everything in one app, but combines password and 2FA in the same vault. If that vault is compromised, you no longer have a real second factor.
Setting up Aegis
These steps follow the screens and labels of Aegis 3.4.3.
- On first start, tap past Welcome to the Security screen. Pick Password, or Biometrics (that sets a password too and adds fingerprint or face unlock). None leaves the vault unencrypted and rules out automatic backups. Aegis warns that if you forget the password, your tokens are gone for good.
- Add accounts with the + button: Scan QR code, Scan image or Enter manually.
- Set up backups (next section) before you remove anything from your old authenticator app.
Already have a setup?
- Aegis on a new phone: on the Welcome screen, tap Import Aegis vault, pick your backup or export file and enter its password. If you used biometric unlock, turn it on again under Settings → Security → Biometric unlock: its key lives in the old phone’s Android Keystore.
- Coming from another app: Aegis’s own hint is to finish setup first. Then open ⋮ → Settings → Import & Export and choose Import from file (pick the app, then its export file) or Import from app (needs root). An unencrypted export file from the old app holds all your secrets in readable form: delete it once the import has worked. From Google Authenticator: in that app, tap Menu → Transfer codes → Export codes (per Google’s help), and scan the QR code or codes with Aegis’s + → Scan QR code.
- Keep the old app until you have signed in to a few services with codes from Aegis and a backup has left the phone.
Backup strategy
Aegis backs up to an encrypted JSON file. Recommended approach:
- Turn on automatic backups: ⋮ → Settings → Backups → Automatically back up the vault. Aegis first asks for a backup strategy (keep Keep a number of versions; Aegis calls Single backup unreliable) and then for a folder. After that it writes a new backup whenever you change something. This only works with an encrypted vault (a password set).
- Get a copy off the phone. Aegis can’t upload anything itself. Have Syncthing sync the backup folder to your computer, or copy the file to an encrypted USB drive now and then. The developers name Nextcloud as the one cloud app they know works as a backup location. Android cloud backups in the same menu is an opt-in alternative that hands the encrypted vault to your phone’s cloud backup.
- Remember the vault password (or your separate backup password, if you set one) and keep a copy of it separately from the backup: the backup can only be opened with it.
Already exporting by hand? Exports and automatic backups produce exactly the same vault file, according to the Aegis FAQ, so switching to automatic backups doesn’t change how you restore. Leave Encrypt the vault ticked when you export (it is on by default): an unencrypted export, which Aegis itself does not recommend, can be read by anyone who gets the file.
If you lose your phone without a backup, you need access via recovery codes — make sure you keep those too for every service where you enable 2FA.
Caveats
Android only: Aegis is the best TOTP app in this lane, but only if you are already on Android. If you need the same setup across Android and iPhone, this is not that product.
Backup discipline is non-optional: The whole privacy advantage of no cloud dependency also means there is no safety net. If you do not set up backups and get a copy off the phone, you are trading convenience away without actually reducing your risk.
TOTP is not the top tier for every account: Aegis is excellent for TOTP, but high-value accounts should still move to hardware keys where supported. This is the best software authenticator in its category, not the end of the 2FA story.
Download
- F-Droid — recommended, no Google dependencies
- Google Play Store
- GitHub APK — direct download
Google Play and GitHub releases are signed with the same developer key; the developers publish its fingerprint and an apksigner check in the README. F-Droid builds and signs Aegis itself, so moving between the F-Droid version and the Play/GitHub version means uninstalling: restore from a backup afterwards.
On GrapheneOS
Aegis doesn’t use Google Play Services: its build has no Google Play Services or Firebase libraries, and F-Droid, which builds it from source, doesn’t allow them. So it runs on GrapheneOS without Google Play installed. Install via F-Droid or the APK from GitHub.
Pros and cons
Pros
- Encrypted local backup with a password you choose — no cloud connection required
- No cloud connection or account required — no risk of third-party lockout
- Biometric unlock (fingerprint or face recognition) with tokens encrypted until unlock
- Imports from many other authenticator apps
- Available on F-Droid — no Google dependencies, runs on GrapheneOS without Google Play
Cons
- Android only — no iOS version, and the developers have no plans for other platforms
- You are responsible for keeping the backup safe; losing both phone and backup means losing 2FA access
- No sync between devices; automatic backups only leave the phone through another app (Syncthing, Nextcloud) or Android’s cloud backup
- Two-person project with a slow release pace (two releases in the past twelve months)
- Biometric unlock doesn’t work on some phones
Conclusion
Aegis is the best TOTP authenticator for Android. Encrypted, open-source, no cloud connection, simple backup. There is no reason to use Google Authenticator or Authy if you’re on Android.
Next step
Choose this if…
Choose Aegis if you are on Android and want an encrypted, offline 2FA app with no cloud connection.
- Two-factor authentication guide — which services to prioritise for 2FA and how to set them up
Already have this?
Turn on automatic backups, make sure a copy leaves your phone, and keep your vault password (or separate backup password) in a different place from the backup itself. Check that you’re on version 3.4.3 or later.
- Bitwarden review — password manager used alongside Aegis
Want to go further?
- YubiKey vs Nitrokey review — hardware 2FA for higher profiles